Showing Posts From
Predictiveanalytics
-
 Amara Singh
- 16 Sep, 2026 21:21
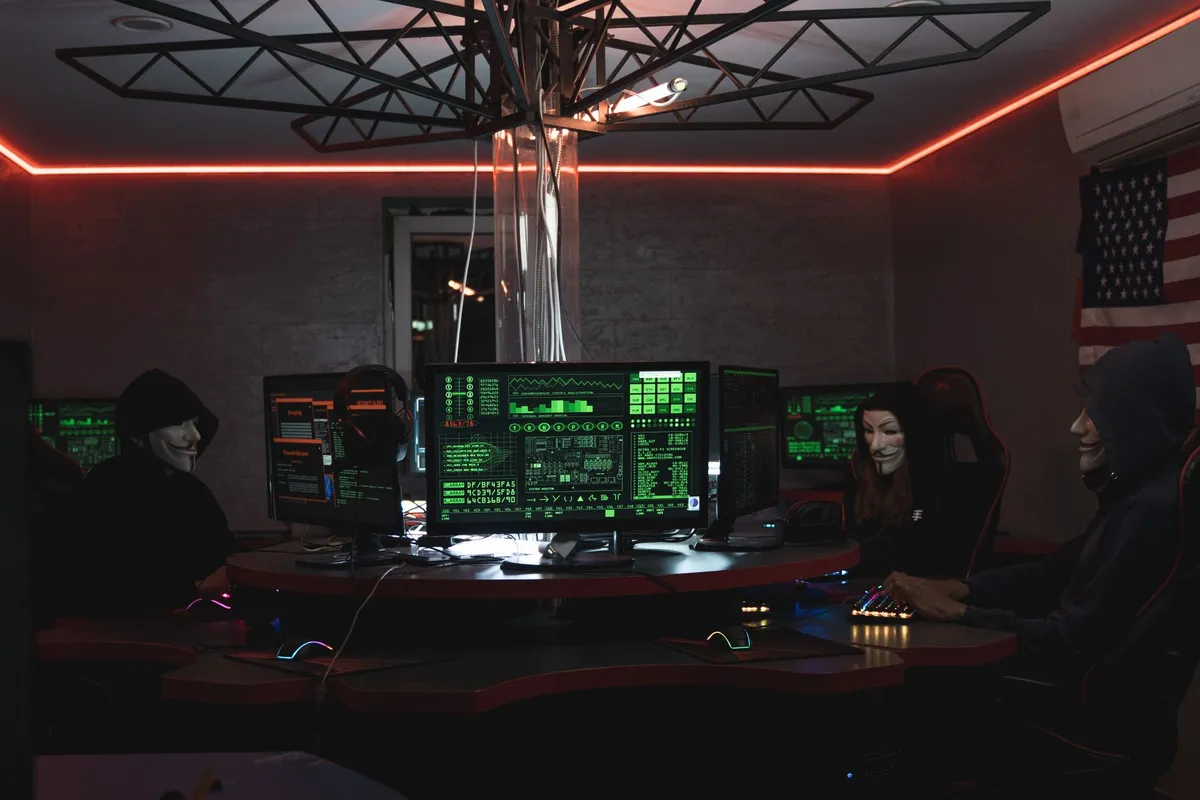
The Silicon Sentinel: Architecting Predictive AI for Proactive Cyber Defense
The Dawn of Algorithmic Vigilance We are currently navigating a paradigm shift in the digital landscape where the speed of attack innovation outpaces the human capacity for response. The traditional castle-and-moat security model is fundamentally obsolete, crumbling under the weight of polymorphic malware, AI-driven social engineering, and zero-day vulnerabilities that manifest in seconds rather than days. As a senior engineer and researcher, I have watched the evolution of threat actors from manual script-kiddies to sophisticated, LLM-augmented syndicates that utilize generative adversarial networks (GANs) to bypass heuristic detection engines. The defense against this onslaught cannot be manual; it must be algorithmic. We are moving toward a future defined by "Predictive Cyber Immunity." This concept moves beyond passive monitoring—what we historically termed SIEM (Security Information and Event Management)—and pivots toward active, Bayesian-probabilistic threat anticipation. By leveraging high-dimensional feature engineering on network telemetry, we can now map the intent of an adversary before the payload is ever executed. This is not merely about identifying a known signature; it is about predicting the behavioral trajectory of a threat actor moving laterally through a Kubernetes cluster or exfiltrating sensitive blobs from an S3 bucket. In this deep dive, we explore how to transition from static defensive posture to dynamic, AI-native threat anticipation, ensuring that our systems do not just detect intrusions, but anticipate them with sub-millisecond precision.Implementing Bayesian Inference for Lateral Movement Detection The primary challenge in modern threat detection is the "signal-to-noise" ratio. In an enterprise environment, millions of log lines are generated every second. Traditional static rules fail because they lack context, leading to "alert fatigue"—the silent killer of effective SOC (Security Operations Center) teams. To combat this, we implement Bayesian inference models designed to calculate the probability of lateral movement based on historical user behavior baselines. When a user initiates an SSH session or triggers a kubectl exec command, the system must evaluate not just the command itself, but the historical drift from the user’s identity profile. If a developer who typically queries SQL databases suddenly initiates reconnaissance commands (e.g., nmap or netstat), a predictive model assigns a high-risk probability score. This is where we shift from binary "Yes/No" alerts to a continuous "Risk Confidence Index." By utilizing Scikit-learn or custom PyTorch transformers, we can build a sliding window that captures sequential event patterns, effectively turning log streams into temporal sequences that reflect intent rather than just action. The following Python snippet demonstrates the construction of a basic anomaly score generator using Gaussian distribution baselines. import numpy as np from sklearn.ensemble import IsolationForest# Simulated user behavior telemetry: [time_delta, connection_frequency, privilege_escalation_score] # Data is normalized to provide a feature set for the anomaly detector telemetry_data = np.array([ [0.1, 12, 0.0], [0.2, 14, 0.1], [0.9, 85, 0.8], # Anomaly: High frequency and high privilege score [0.1, 10, 0.0] ])def evaluate_threat_risk(features): clf = IsolationForest(n_estimators=100, contamination=0.1) clf.fit(features) # Scores: -1 indicates an anomaly, 1 indicates normal behavior risk_scores = clf.predict(features) return risk_scores# Execution flow: analyzing a batch of network events predictions = evaluate_threat_risk(telemetry_data) for i, status in enumerate(predictions): if status == -1: print(f"CRITICAL: Anomaly detected in event stream at index {i}. Triggering automated isolation protocol.")Leveraging Graph Neural Networks for Topology-Aware Defense Static perimeter security assumes a clean division between "inside" and "outside." In the era of microservices, distributed cloud infrastructure, and ephemeral serverless functions, the "inside" is a complex graph of interconnected dependencies. Threat actors exploit this by mapping internal trust relationships. To neutralize this, we deploy Graph Neural Networks (GNNs). A GNN views your infrastructure as a series of nodes (containers, services, users) and edges (API calls, data flows). By training on the graph topology, the AI learns the "normal" communication patterns between services. If Service A suddenly attempts to invoke an administrative API on the Kubernetes control plane—an interaction that never existed in the historical graph—the GNN detects a structural anomaly in the network graph. This is vastly superior to traditional regex-based filtering, as it accounts for the context of the connection. For instance, if a public-facing web server attempts to query the metadata service for AWS IAM roles (a common precursor to SSRF attacks), the GNN identifies this as a "topology violation" and can trigger an immediate egress block. Integrating this at the Envoy proxy level or via service mesh policies (e.g., Istio) provides a layer of defense that is invisible to the attacker but deeply rooted in the architecture of your distributed system.Orchestrating Automated Remediation via Infrastructure-as-Code Detection is only the first step. In the face of a zero-day exploit, human response times are measured in minutes, whereas modern machine-speed attacks operate in milliseconds. We must integrate our predictive models with orchestration engines to enable "Self-Healing Infrastructure." When an AI agent predicts a high probability of attack, it should not just send a Slack notification; it should execute a pre-configured playbook to segment the affected network zone, rotate compromised credentials, or increase logging verbosity on the suspected nodes. The following YAML configuration demonstrates a defensive policy definition for a Kubernetes-native environment using a hypothetical "AI-Security-Controller" that interacts with the cluster to enforce ephemeral network policies during a high-risk event. apiVersion: security.amara.io/v1alpha1 kind: ThreatResponsePolicy metadata: name: preemptive-node-isolation spec: trigger: "anomaly_score > 0.85" actions: - isolate_pod: selector: "app=exposed-web-gateway" gracePeriod: 0 - rotate_secrets: target: "db-credentials" scope: "namespace-wide" - notify: slack_channel: "#incident-response" contingency: revert_policy: "manual_approve_only"The Role of Generative Adversarial Networks in Red Teaming We cannot build resilient models without first stress-testing them against adversarial generation. Here, I advocate for the usage of GANs in the development pipeline to simulate "Next-Gen" cyber attacks. A GAN consists of two neural networks: the Generator, which produces synthetic malicious traffic, and the Discriminator, which acts as the defensive AI. By allowing these two networks to iterate against each other, the defender (our IDS/IPS system) evolves more rapidly than any human red team could manually induce. These generative models can craft polymorphic obfuscation techniques for payloads, effectively creating training datasets that mimic the evolution of real-world malware. This approach ensures that when a real threat emerges, our models have already "seen" a synthetic precursor to that attack. It is crucial, however, to ensure that the synthetic data maintains statistical alignment with actual production traffic; otherwise, you risk a high False Positive rate that can lead to service outages. The key is in the "Reward Function"—ensure your GAN is incentivized to produce attacks that mimic actual adversarial intent, such as exfiltration patterns, rather than just random noise.Operationalizing Threat Intelligence Feeds with Vector Databases Modern threat anticipation relies on the ability to query vast, unstructured datasets containing millions of IOCs (Indicators of Compromise). Traditional relational databases fail to handle the vector embeddings of these threats. By implementing vector databases (such as Pinecone or Milvus), we can store threat telemetry as multi-dimensional vectors. When a new file hash or IP reputation score enters the threat intel feed, we perform a nearest-neighbor search to see if this new threat is "contextually similar" to known attack campaigns. This allows for the rapid identification of "family members" of malware. Even if an attacker re-compiles their binary to change the file hash, the vector representation (the core behavioral pattern or code structure) remains relatively stable in embedding space. This allows security teams to build a living knowledge graph of threat actors, enabling proactive hunting across the entire organization. By automating the ingestion of these feeds into a vector-searchable index, we bridge the gap between global threat intelligence and localized, machine-speed defense. Designing for Resilience in the Era of Machine Intelligence As we transition toward these predictive, AI-driven architectures, we must remain cognizant of the ethical and operational risks inherent in automated security. We are delegating critical decision-making—who gets blocked, what traffic is dropped, and which nodes are quarantined—to machines. This introduces the risk of "Model Drift," where the security AI begins to perceive legitimate traffic as malicious due to changes in user behavior or application updates. Furthermore, we must design our systems to be "Human-in-the-loop" capable. Even the most sophisticated predictive model should provide a human-readable explanation for its decisions, leveraging Explainable AI (XAI) techniques like SHAP (SHapley Additive exPlanations) or LIME. When a system triggers a critical isolation event, the security engineer must be able to instantly query: "Why was this node flagged?" The answer should not be a black box, but a list of feature contributions that influenced the score. The architecture of the future is not about building stronger firewalls; it is about building more intelligent observers. It is about understanding the "intent" of the digital flow, identifying the precursors to chaos, and intervening with the precision of a surgeon. We are moving away from the era of "Detection after the fact" and into the era of "Anticipation as a default." As we continue to iterate on these models, the integration between DevOps and Security (DevSecOps) must evolve into an "AI-DevSecOps" model, where the security policy is as dynamic as the code itself. Every deployment should carry its own defensive model, a "Security Twin" that monitors its state against anticipated threats. We are the architects of this digital immune system. By combining graph-based analytics, Bayesian inference, and adversarial testing, we create not just a secure system, but a resilient one. The path forward is difficult, laden with technical debt and architectural complexity, but it is the only path that ensures the integrity of our global infrastructure in an era where software is, quite literally, the foundation of civilization. Stay vigilant, stay technical, and keep your models sharp. #AI #Cybersecurity #DevOps #MachineLearning #PredictiveAnalytics #CloudSecurity #InfoSec Related InsightsQuantum Sensing: The Subatomic Microscope Reshaping Mineral Exploration Decentralized Carbon Credit Tracking: Harnessing Distributed Ledger Technology for a Sustainable Future Taming the Hallucinations: An In-Depth Analysis of Retrieval-Augmented Generation (RAG) Architectures{ "@context": "https://schema.org", "@type": "FAQPage", "mainEntity": [ { "@type": "Question", "name": "What is the main focus of The Silicon Sentinel: Architecting Predictive AI for Proactive Cyber Defense?", "acceptedAnswer": { "@type": "Answer", "text": "Amara Singh explores the technical frontier of predictive AI, detailing how machine learning models are shifting cybersecurity from reactive patching to preemptive neutralization." } }, { "@type": "Question", "name": "Who authored the comprehensive guide on The Silicon Sentinel: Architecting Predictive AI for Proactive Cyber Defense?", "acceptedAnswer": { "@type": "Answer", "text": "This detailed article and its insights were carefully researched and authored by Amara Singh." } }, { "@type": "Question", "name": "Where can I find more related content about Technology?", "acceptedAnswer": { "@type": "Answer", "text": "You can explore more articles, detailed reviews, and similar insights by browsing the Related Insights section at the bottom of this article or visiting our dedicated Technology category page." } } ] }